MCP Gateway
Control AI Agent Actions with Traefik Hub MCP Gateway
Enforce task, tool, and transaction-level access on every agent call, with runtime guardrails on agent tool calls, and a verifiable record of every allow and deny.
TRAEFIK LABS IS TRUSTED BY LEADING ENTERPRISES WORLDWIDE
MCP Gateway 101
What is an MCP gateway?
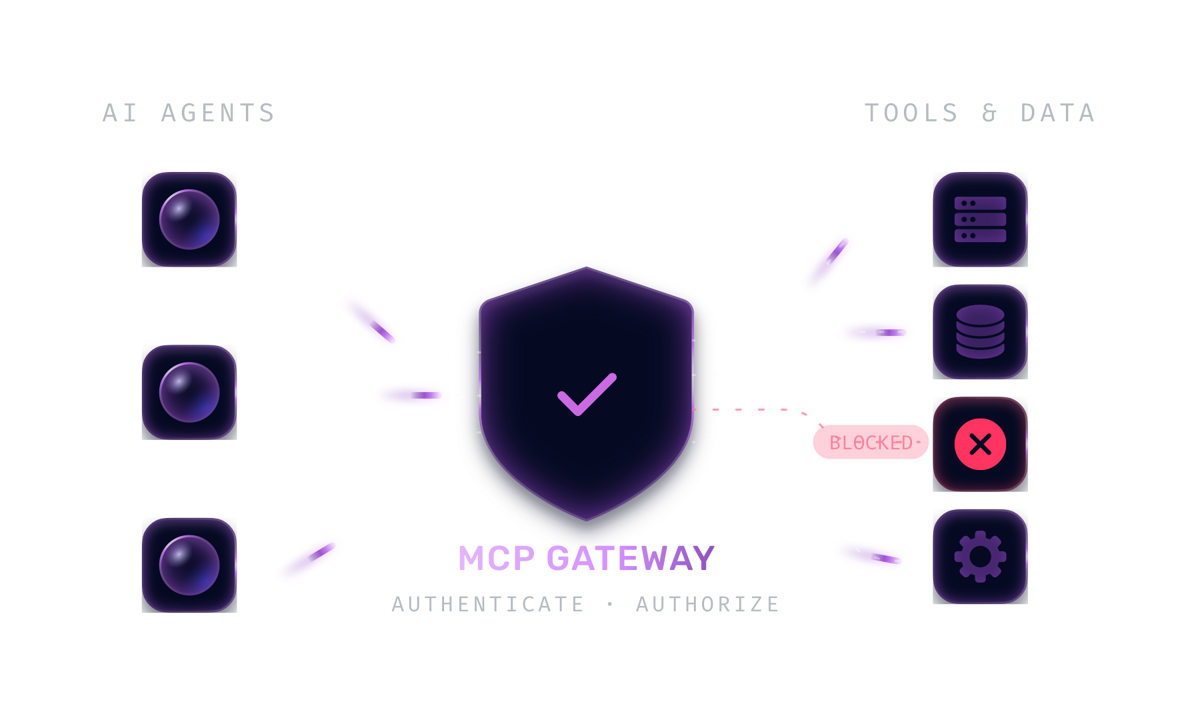
An MCP gateway is a policy enforcement point between AI agents and Model Context Protocol (MCP) servers. It authenticates each request, decides which tools and data an agent can use, and records the decision.
Challenges
Why Do MCP Connections Need a Gateway?
MCP defines how agents connect to tools. Without a gateway, whoever runs the servers handles access decisions, session routing, and governance.
Agents Get More Access Than Their Task Needs
An agent with a valid credential can call any tool the server exposes. Those credentials also end up copied into agent code, CLIs, and notebooks.
Governance is Siloed and After the Fact
ACLs and generic API gateways aren't designed to enforce agent-centric access control. Tool-by-tool rules have no central review or versioning, and observability is split across logs and teams.
Agent Actions Can't Be Proven in an Audit
Traces are sampled, filtered, and can be altered by whoever operates them. When an auditor asks months later who authorized an action, under which policy, and whether the record has changed since, a trace can't answer.
The Solution
Introducing Traefik Hub MCP Gateway
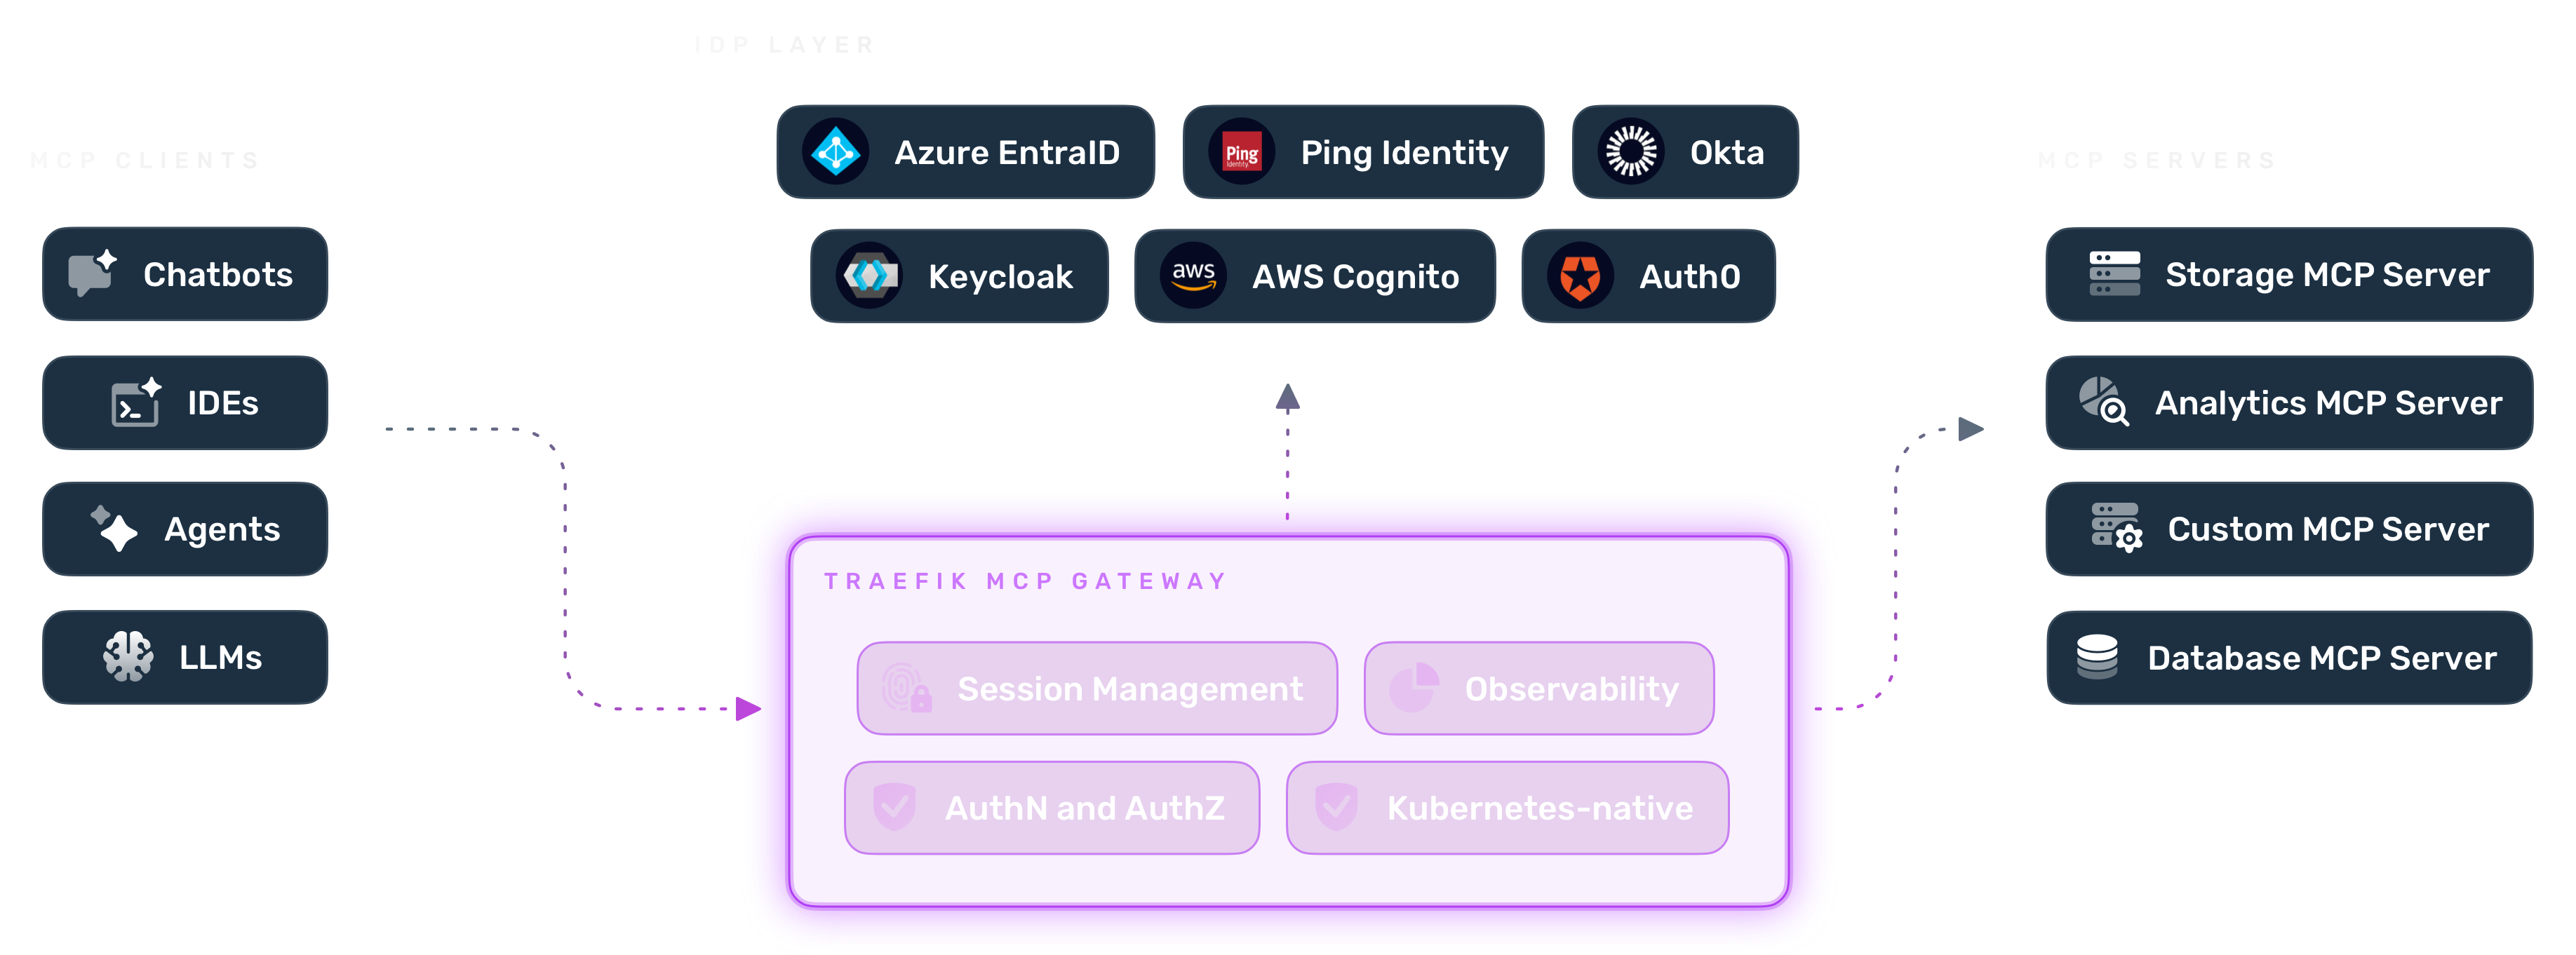
Traefik Hub MCP Gateway extends Traefik Hub API Gateway, so API, AI, and MCP traffic run through a single binary. It sits between MCP clients and MCP servers as the data and control plane, runs on any orchestrator (self-hosted or air-gapped), and enforces Task-Based Access Control (TBAC) on every request.
Task, Tool, & Transaction-Based Access Control (TBAC)
Authorize each request by task, tool, and transaction, down to individual tool arguments
Compare arguments to JWT claims at runtime, such as capping
approve_expenseat each agent'sapproval_limitIsolate tenants with a single rule using variable substitution
Deny any request that matches no policy, by default
Filter
tools/list,prompts/list, andresources/listso agents only see the tools they can use
Authentication and Runtime Policy Guardrails
Validate JWTs as an OAuth 2.1 and OAuth 2.0 resource server
Publish authentication metadata and
WWW-AuthenticatechallengesInject upstream API keys, with optional On-Behalf-Of forwarding and token exchange support
Apply rate, concurrency, time-window, and query-pattern limits
Add optional topic, PII, and jailbreak controls
Evaluate TBAC policies using JWT claims and MCP attributes
Manage YAML policies through GitOps review and promotion
Deny unmatched requests with configurable messages
Session-Smart Load Balancing
Server-side session affinity keeps long-running conversations on the same pod
Separate read and write pools protect systems of record
Deterministic routing maintains session affinity through rollouts and autoscaling
Stable routing helps reduce failed sessions, retries, and duplicate writes
Observability and Verifiable Audit
OpenTelemetry metrics and traces tagged by MCP method, tool, prompt, and resource URI
Tool-call arguments stay out of traces unless you opt in
Export to Grafana, Datadog, Dash0, or any OpenTelemetry backend
PII masking and blocking with content guards
Append-only, witness-cosigned evidence of every allow and deny, verifiable on your infrastructure
Compare
How Traefik Hub MCP Gateway Compares
| Apigee | Traefik Hub MCP Gateway |
|---|---|
| Best for | |
| Satisfied Google Cloud teams exposing existing Apigee APIs as MCP tools | Kubernetes teams needing argument-level policy. Best for self-hosted or air-gapped deployments. |
| Access scope | |
| API products listing allowed tool operations per OAuth client | Agent identity, task, tool, resource URI, tool arguments |
| Conditions on tool arguments | |
| Not documented | Numeric and string conditions evaluated against JWT claims |
| MCP content guardrails | |
| Not documented for MCP proxies; Model Armor policies cover LLM prompts and responses | PII detection, masking, and blocking plus semantic checks via external guard models, on tool arguments and results |
| MCP observability | |
| Apigee Analytics | OpenTelemetry metrics and traces; tool arguments opt-in |
| Tamper-evident agent evidence | |
| Not documented; Cloud Audit Logs cover admin and data access activity | Immutable, witness-cosigned transparency log of gateway approvals and denials |
| Deployment | |
| Apigee SaaS or hybrid | Self-hosted Kubernetes, air-gapped capable |
Based on vendor documentation reviewed in September 2026. “Not documented” means the capability did not appear in the documentation reviewed. For MintMCP, TrueFoundry, and Docker MCP Gateway, see Best MCP Gateways 2026.
Frequently Asked Questions
Traefik Hub MCP Gateway supports Streamable HTTP, the MCP specification's transport for remote servers. The standalone HTTP+SSE transport was deprecated in the 2025-03-26 spec revision, so the gateway doesn't support it. Server-sent event streams within Streamable HTTP responses are supported.
What Users Have to Say
Ready to get started?
See how Traefik Hub MCP Gateway aligns to your requirements in a personalized demo or test drive it yourself with a free trial.